


 Email
 SMS
 Whatsapp
 Web Push
 App Push
 Audience Sync for Ads
 Popups
 Channel A/B Testing
 Control groups Analysis
 Frequency Capping
 Funnel Analysis
 Cohort Analysis
 RFM Analysis
 Signup Forms
 Surveys
 NPS
 Landing pages personalization
 Website A/B Testing
 PWA/TWA
 Heatmaps
 Session Recording
 Wix
 Shopify
 Magento
 Woocommerce
 eCommerce D2C
 Mutual Funds
 Insurance
 Lending
 Recipes
 Knowledgebase
 Developer Docs
 Product Updates
 App Marketplace
 Academy
 Ebooks
 Case Studies
 Blog
 Templates
 Bhivesh Madaan
- What PII masking and tokenisation mean and how they work
- Why PII protection matters and how masking and tokenisation differ
- How to choose the right PII protection strategy and stay ahead of privacy trends
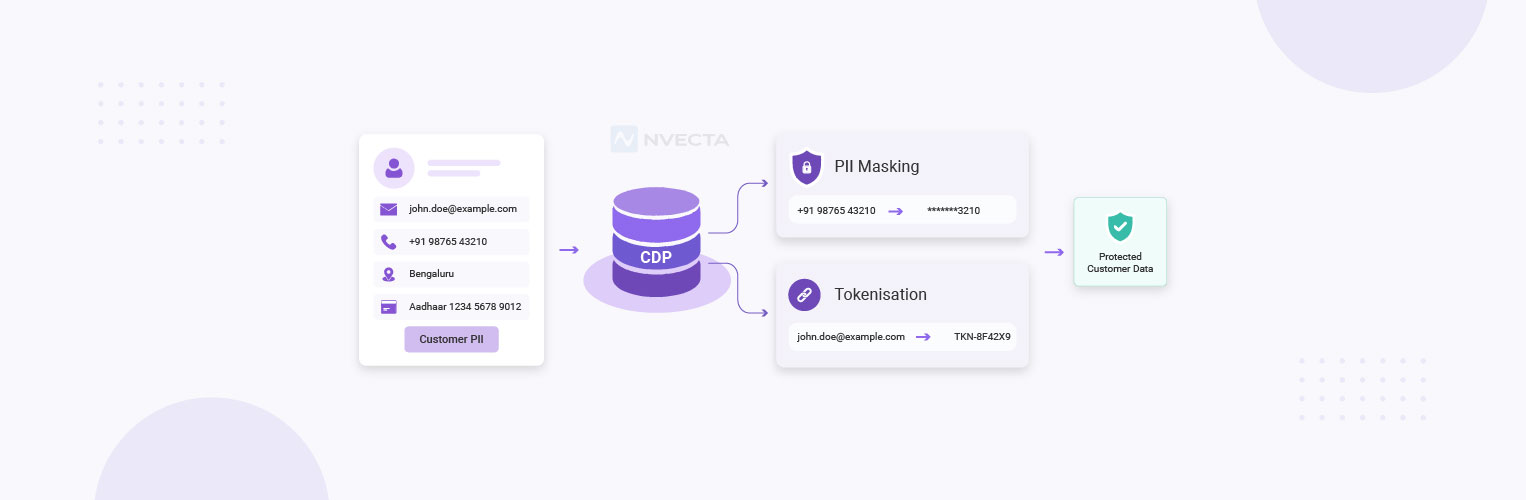
- How NVECTA CDP applies masking and tokenisation across the customer data
What Is PII Masking?
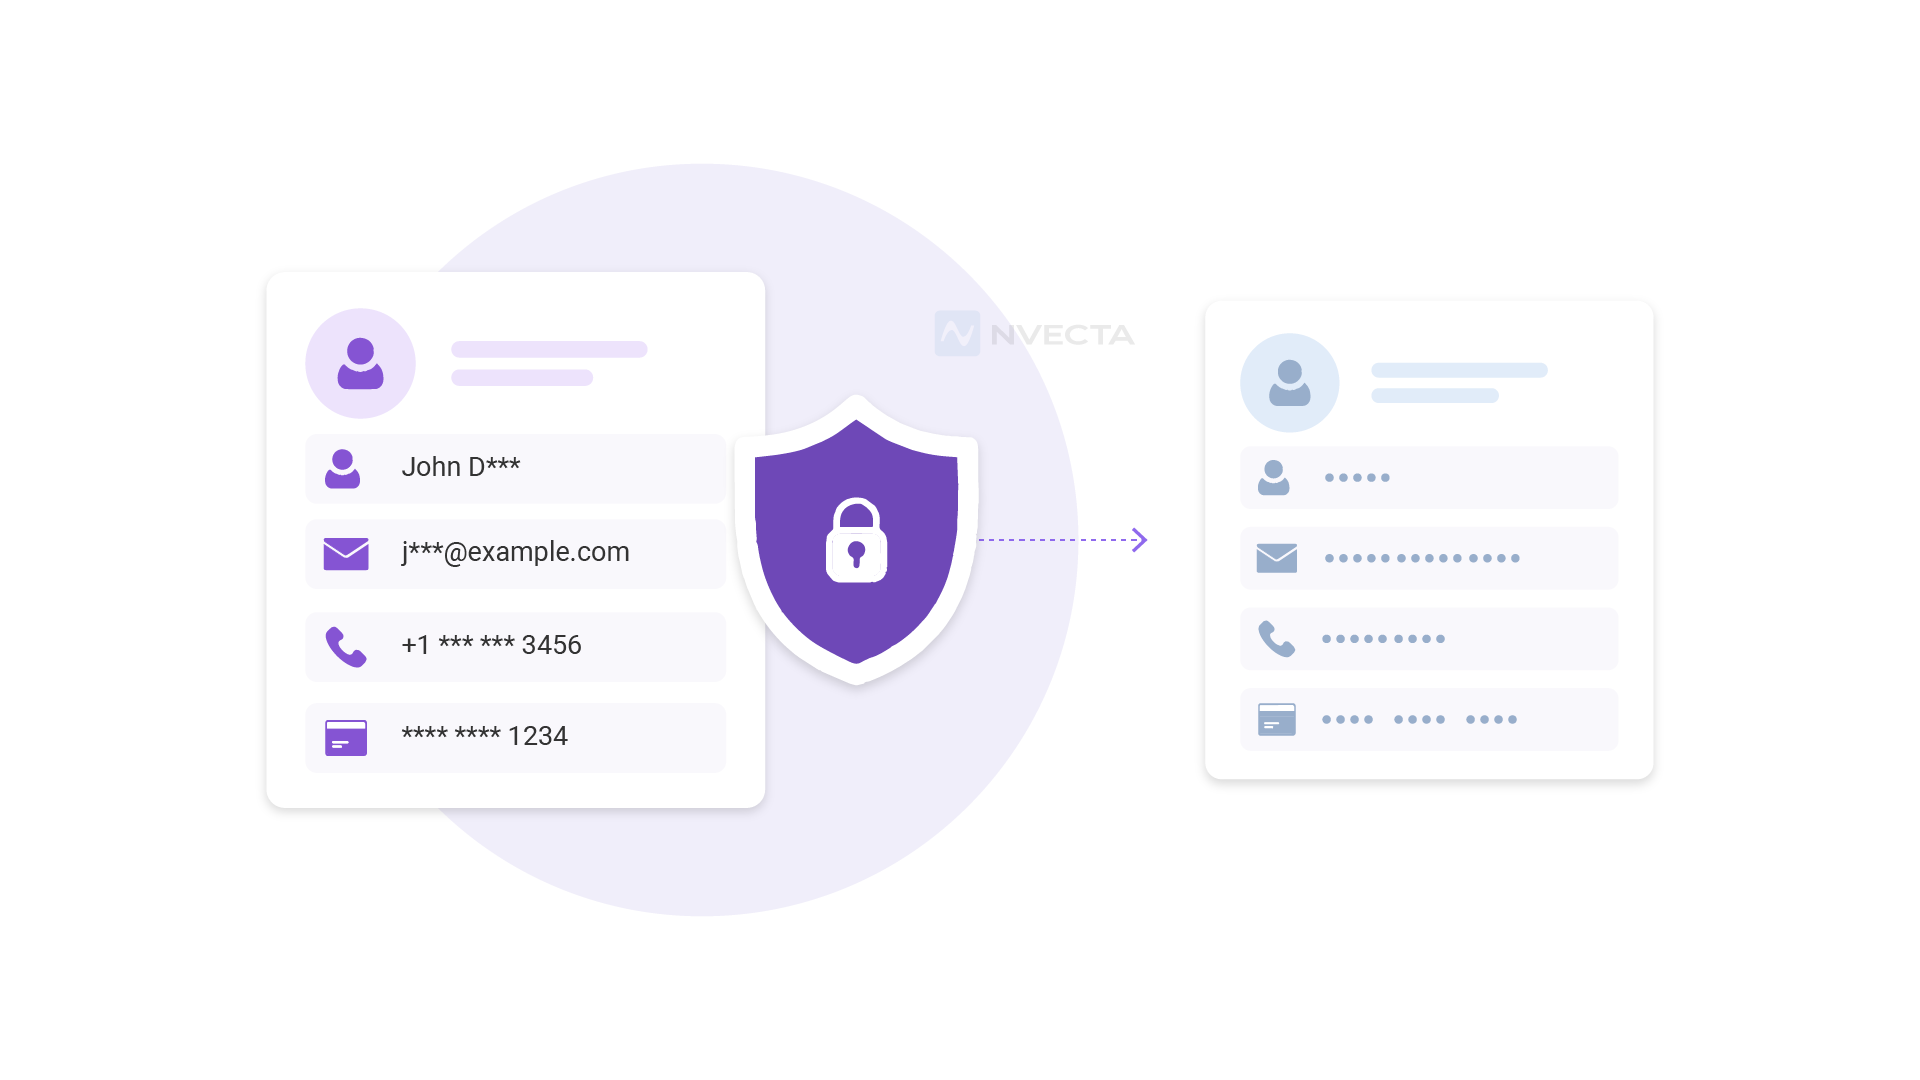 PII masking hides sensitive personally identifiable information (PII) to protect user/customer identities and comply with data security and privacy laws. This lets data stay useful without revealing the real value. A marketer can segment users by city without ever seeing a real address.
Static vs Dynamic Data Masking
Static masking changes data once, usually before it moves to a test environment or a shared dataset. The original value is gone for good in that copy. Dynamic masking works differently. It hides or reveals data at the moment someone queries it, based on their role. An admin might see the full email address. A support agent might only see the domain. Most data teams now lean on dynamic masking, since access needs shift by role and by task.What Is PII Tokenisation? Definition and How It Works
PII Tokenisation replaces sensitive data with a digital identifier, called a token, so as to protect essential information when it comes to security or usability. A sensitive value, like a credit card number or a government ID, can be replaced with a random string – a token. The token carries no meaning on its own.Token Vaults and the DeTokenisation Process
Every token connects back to its original value inside a secure vault. Only systems with the right permissions can use that vault and retrieve the real data information through a process called detokenisation. The sensitive data is stored in one place, so that every other system in the stack works with tokens that carry no sensitive data values.Why PII Protection Matters More as Customer Data Scales Across Systems
Customer data protection isn’t a single decision anymore. The same customer profile now feeds identity resolution, marketing tools, analytics dashboards, support software, and AI features, often within the same day. Organizations can also work with a penetration testing company to identify exploitable weaknesses across applications, integrations, APIs, and access controls that could expose sensitive customer data.The Risk of Static, One-Time Protection
A protection method applied once, at the moment data enters a system, can’t account for every place that data travels next. A field masked for one team might sit fully exposed in another tool it gets exported to. Each new integration adds another access point, and a fixed rule set can’t keep pace with how fast that list grows.Why Dynamic, Context-Aware Controls Are Becoming Essential
Dynamic controls, sometimes called role-based access control, check who’s asking for data and why, every time someone asks. The same field can show up masked for one user and fully visible for another, based on role and task. Access needs are rarely permanent. A contractor on a short project needs different visibility than a full-time analyst. A fixed rule can’t serve every case, which is why the decision has to happen at the exact moment data gets accessed.PII Masking vs Tokenisation: Key Differences
The core difference is simple. Masking changes how data looks without removing the original. Tokenisation removes the original entirely and replaces it with a separate reference.| Factor | Data Masking | Data Tokenisation |
| Reversibility | Not reversible by default, but policy exceptions can reveal real data | Reversible through a secure vault |
| Applied | At the point of use, when data is queried | At the point of entry, before data is stored |
| Performance | Minimal impact on standard queries | Can slow down joins and searches on tokenised fields |
| Flexibility | High. Different users can see different levels of detail | Low. Access is largely on or off |
| Regulatory fit | Strong for GDPR, CCPA, and analytics-heavy compliance needs | Strong for PCI DSS and data with no analytical value |
| Typical use case | Dashboards, segmentation, AI training, testing | Payment data, government IDs, highly regulated fields |
Choosing the Right PII Protection Strategy for Your Business
The right strategy comes down to two questions: how sensitive is the field, and does any system need the real value back? Fields with low risk and daily use fit masking. Fields with high risk and rare use fit tokenisation. Many businesses need both, applied field by field. Organizations can also work with a penetration testing company to identify exploitable weaknesses across applications, integrations, APIs, and access controls that could expose sensitive customer data.When to Choose Data Masking
Mask fields your teams use for everyday work, like names, emails, and locations in dashboards, campaigns, or AI training data. Masking keeps these fields useful while limiting who sees the real value. Masking also fits testing and development environments well, since developers rarely need real customer data to build and test features.When to Use Tokenisation
Tokenise fields with high risk and little analytical value, like credit card numbers, bank account details, and government IDs. Nobody needs to see a real SSN to run a customer segment. Tokenisation also fits when a strict regulation, like PCI DSS, expects the data to sit outside your main systems in a separate, controlled vault.When to Use Both
Most businesses end up layering the two, field by field. A customer record might tokenise the payment ID while dynamically masking the email address based on who’s viewing it. Each field gets the protection level it needs, rather than one method applied across every field.PII Protection Trends and Regulations to Know in 2026
The biggest shift in 2026 comes from AI. Agents and copilots now query customer data directly to personalise offers, answer support tickets, and automate tasks that used to need a person in the loop.How AI Agents and Personalisation Are Changing PII Exposure
Every AI feature that touches customer data is a new access point. An agent retrieving a customer’s order history for a support chat can, without the right controls, grab far more personal detail than the task needs. AI systems chain requests across multiple sources in seconds. One weak control point can expose more data, faster, than a manual process ever could.Evolving Data Privacy Regulations
Regulations keep tightening the space businesses work in. GDPR (General Data Protection Regulation) enforcement in the EU has grown stricter around cross-border transfers and data residency. US states keep adding privacy laws that push for data minimisation. India’s DPDP (Digital Personal Data Protection Act) adds fresh obligations for any business handling Indian customer data.Why Businesses Are Combining Masking and Tokenisation
More businesses now run masking and Tokenisation together, layered by how sensitive each field is. Highly sensitive fields like SSNs get tokenised. Fields used for daily analytics get masked dynamically based on who’s asking. This gives businesses strict protection for their riskiest data and flexibility for the data teams use daily.How NVECTA Applies Masking and Tokenisation Across the Customer Data Lifecycle
NVECTA is an AI-powered customer data platform built for effective data handling while staying compliant with data protection laws. It serves multiple business models and protects each one’s customer data through masking and tokenisation, applied based on how sensitive that data is.Protect Sensitive Customer Data Without Losing Its Context
NVECTA masks and tokenises data without breaking its structure. A masked email still looks like an email. A tokenised account number still fits the field format your systems expect. Teams keep running the same reports and workflows on protected data without rebuilding anything.Control Access to PII With Dynamic Data Masking
NVECTA applies masking at the point a user queries the data, not once at ingestion and never again. A campaign manager sees a masked phone number. A data engineer with the right permission sees the real one. Access rules live in policy, not in code. Teams change who sees what without touching a pipeline or waiting on an engineering ticket.Replace Sensitive Identifiers With Tokens When Needed
For fields that carry real risk, like payment IDs or government identifiers, NVECTA tokenises the value and stores the mapping in a secure vault. No other part of the platform holds the real value. DeTokenisation only happens through a controlled request, scoped to the exact system and purpose that needs it. Nothing retrieves the real value by default.Keep Customer Data Protected Across Integrations
Customer data rarely stays inside one platform. NVECTA carries masking and Tokenisation rules with the data as it moves to ad platforms, messaging tools, and other integrations. A destination tool only receives what its policy allows, whether that’s a masked field, a token, or the real value for systems approved to see it.Activate Customer Data Without Unnecessary PII Exposure
When a campaign or an AI feature retrieves customer data for activation, NVECTA checks the policy first. A personalisation engine might get a customer’s product preferences without ever touching their email or phone number. This keeps activation useful without handing every connected system more personal data than the task calls for.Give Teams Visibility and Control Over Customer Data Usage
Every access request, mask applied, and token resolved gets logged in an audit trail. Compliance teams pull a clear record of who accessed what data, when, and under which policy, without digging through separate systems. That’s the difference between scrambling before an audit and being ready for one. The logic stays the same across all six: NVECTA applies protection based on field sensitivity and what the task requires, from the moment data enters the platform to the moment it activates elsewhere.Conclusion
Customer data drives growth, but only when it stays protected. Getting masking and tokenisation right builds customer trust, meets compliance requirements, and lets teams work with data confidently. NVECTA applies both methods together, field by field and role by role. High-risk data like payment details and government IDs stays locked in a secure vault, while every action gets logged for a clear compliance record. See how NVECTA secures your customer data with masking and tokenisation. Book a demo now.Frequently Asked Questions
Is Tokenisation More Secure Than Masking?
Tokenisation removes the real value from your systems entirely, which makes it stronger for high-risk fields like payment data. Masking still protects data well but keeps it usable. The right choice depends on the field and how your teams need it.
Can Tokenised Data Still Be Used for Analytics?
Tokenised data is suitable for basic tracking, such as counting unique users, but offers limited analytical value because original values are no longer available. Masked data often works better for analytics because it preserves the structure and context of original data while hiding sensitive values.
Does Data Masking Alone Satisfy GDPR or CCPA Requirements?
Data masking helps organisations comply with the GDPR and CCPA regulations since it protects the personally identifiable information (PII). However, it does not suffice to meet the requirements, as one has to go further with other processes. The masking fulfills only part of the PII protection rules, and companies must take additional measures such as consent, access control, retention, and other procedures.
What Is the Difference Between Masking, Tokenisation, and Encryption?
Masking hides sensitive data while keeping it usable by different teams across tools and platforms. Tokenisation replaces sensitive data with a random token, with original values stored in a secure vault. Encryption transforms data using a cryptographic key, which authorised users or systems need for access. Each approach serves a different security purpose, and businesses often use them together.
Do Businesses Need Both Masking and Tokenisation?
Most businesses benefit from using both, applied based on how sensitive each field is. High-risk fields like SSNs or payment details fit Tokenisation. Fields your teams use daily, like names or emails in dashboards, fit dynamic masking better.
How Is PII Protection Changing with AI-Driven Personalisation in 2026?
AI agents now query customer data directly to personalise experiences and automate tasks. This adds new access points that older static protection methods weren’t built for, pushing businesses toward dynamic, policy-based controls that check access at the moment data gets used.
How Does NVECTA Decide Which Method to Apply to Which Data?
NVECTA applies protection based on field sensitivity and how the data gets used. High-risk fields with no analytical value get tokenised. Fields teams need for daily work get masked dynamically, based on the user’s role and the specific task at hand.
