


 Email
 SMS
 Whatsapp
 Web Push
 App Push
 Audience Sync for Ads
 Popups
 Channel A/B Testing
 Control groups Analysis
 Frequency Capping
 Funnel Analysis
 Cohort Analysis
 RFM Analysis
 Signup Forms
 Surveys
 NPS
 Landing pages personalization
 Website A/B Testing
 PWA/TWA
 Heatmaps
 Session Recording
 Wix
 Shopify
 Magento
 Woocommerce
 eCommerce D2C
 Mutual Funds
 Insurance
 Lending
 Recipes
 Knowledgebase
 Developer Docs
 Product Updates
 App Marketplace
 Academy
 Ebooks
 Case Studies
 Blog
 Templates
 Jack Harry
What SPF Flattening Is and Why It Matters
Sender Policy Framework (SPF) remains one of the foundational email authentication standards, helping organizations prevent spoofing and domain abuse. An SPF record, published as a DNS TXT record, tells receiving servers which IP addresses are authorized to send emails on behalf of your domain. As your outbound email infrastructure expands—often due to adopting numerous cloud services, third-party email senders, and marketing platforms like Mailchimp, Amazon SES, SendGrid, or Salesforce—the complexity and length of your SPF record frequently increase.
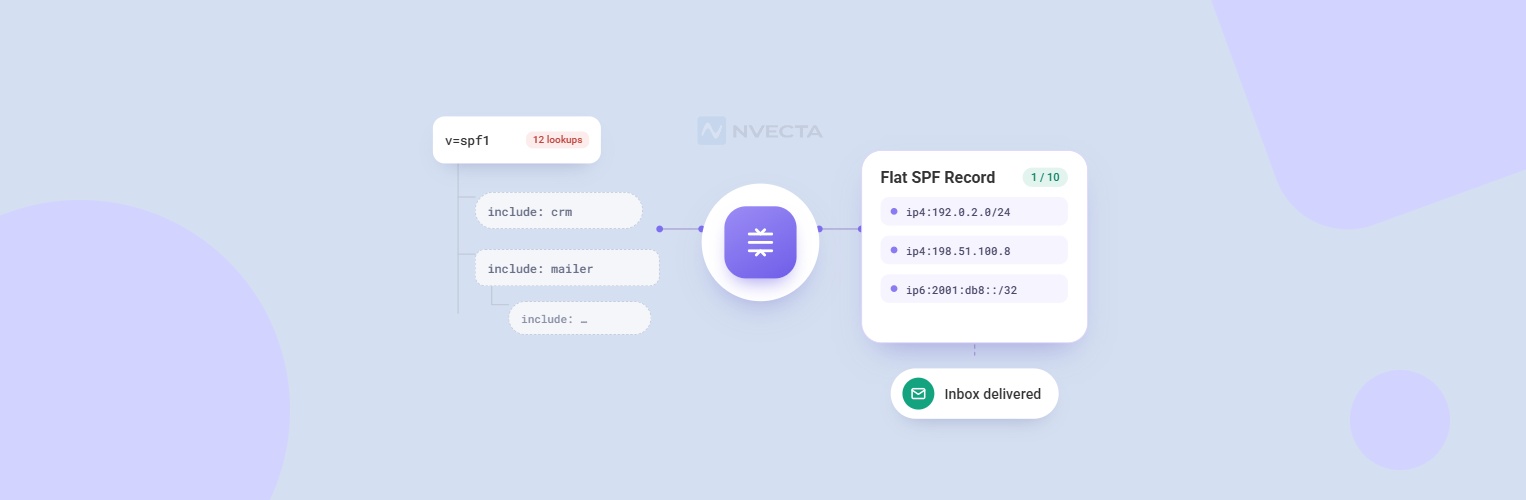
SPF flattening is the process of simplifying an SPF configuration by converting all indirect mechanisms (mainly `include` and nested include mechanisms) into a direct list of resolved IP addresses. By replacing DNS lookups with explicit IP addresses, a flattened SPF record directly lists the outbound IP ranges authorized to send on your behalf.
A comprehensive SPF flattening tool, such as a dedicated SPF flattener, automates this transformation, outputting a “flattened” record suitable for immediate deployment. Hosted SPF solutions and platforms like PowerDMARC, using services such as PowerSPF, routinely leverage this approach to minimize DNS lookups and maintain up-to-date, compliant SPF records via automated updates.
SPF flattening matters because SPF records with excessive DNS lookups expose organizations to SPF failures, silent SPF failures, and deliverability issues, potentially resulting in SPF PermError or permanent error states. A robust flattened SPF record reduces the maintenance burden, enhances email delivery, and ensures alignment with DMARC policy enforcement.
How SPF Lookup Limits Affect Email Deliverability
Understanding the 10-Lookup Limit
The SPF standard, formalized by RFC 7208, imposes a strict SPF lookup limit: no more than ten DNS lookups are permitted per SPF check (including `include`, `a`, `mx`, `ptr`, and `exists` mechanisms). Exceeding this 10-lookup limit leads to a PermError (permanent error) in SPF authentication, which can silently block legitimate email traffic—especially critical for high-volume senders using multiple email vendors and marketing platforms such as Google Workspace, Microsoft 365, Zoho, or Mandrill.
Impact on Email Deliverability
When SPF validation fails—either due to an overly complex SPF record, excessive record bloat, or an untouched nested include chain—major receivers like Outlook.com, Gmail, and others may reject emails or send them to spam. These SPF failures can be silent, surfacing later in aggregated DMARC reports or directly impacting SPF pass/fail rates. An SPF audit using an SPF checker or DMARC reporting tool frequently uncovers these bottlenecks, revealing how improper SPF management impairs email delivery and authentication standards adherence.
Common Causes of Failures
Frequent causes of SPF validation failures include:
- Long chains of `include` or nested include mechanisms referencing third-party email vendors (e.g., Zendesk, SendGrid, Amazon SES).
- Frequent IP address changes by cloud services and CRM tools, requiring manual SPF record updates.
- Outdated DNS TXT records with redundant or deprecated IP addresses.
- Overlapping outbound IP ranges between multiple service providers.
When You Should Consider Flattening Your SPF Record
Key Indicators for SPF Flattening
SPF flattening becomes essential under several scenarios:
- Approaching or exceeding the SPF 10-lookup limit: If an SPF checker or an SPF audit indicates more than ten DNS lookups, flattening your SPF record becomes critical to maintain deliverability.
- Dependence on numerous third-party email senders: Organizations leveraging multiple marketing and automation platforms, from Mailchimp and Mandrill to Salesforce or CRM tools, often hit lookup limits due to numerous nested includes.
- Frequent changes in your provider ecosystem: If your email vendors or service providers are regularly modifying outbound IP addresses, static SPF flattening must be paired with automatic updates or dynamic SPF flattening to prevent SPF failures.
- Complex SPF configuration: Overly complicated SPF records not only introduce potential validation failures but also increase the risk of maintenance errors, inadvertently causing SPF PermError or permanent error states.
Risks of Ignoring SPF Flattening
Failure to address SPF lookup limits can result in:
- Silent SPF failures: These can go unnoticed but significantly impact your DMARC policy enforcement, leading to email delivery issues.
- SPF PermError or permanent error: Directly reducing SPF pass/fail rates and potentially compromising SPF alignment with DKIM and DMARC.
- Record bloat and character limit exceedance: DNS TXT records exceeding the 255-character limit may be truncated, causing partial SPF configuration and additional validation failures.
Step-by-Step Guide to Safely Flattening an SPF Record
Step 1: Perform an SPF Audit
Begin by running a comprehensive SPF audit using an SPF checker or reporting tool (such as PowerDMARC dashboard). This highlights all DNS lookups, the use of SPF Macros, nested include mechanisms, and potential SPF failures in your current SPF record.
Step 2: Choose Your SPF Flattening Strategy
- Manual Flattening: Manually resolve and replace all include mechanisms with their respective IP addresses. This static SPF flattening approach can be effective for smaller, less dynamic infrastructures but introduces a significant maintenance burden when providers change their outbound IP ranges.
- Automated/Hosted SPF: Employ an SPF flattening tool—such as PowerSPF or other hosted SPF services—capable of periodic automatic updates. Such a solution provides dynamic SPF flattening, reducing risk by accommodating regular provider IP changes.
Step 3: Use an SPF Flattener Tool
Input your existing SPF record into a trusted SPF flattener. Tools like PowerSPF or other industry-leading flattening solutions will:
- Resolve all `include` and nested include mechanisms.
- Aggregate all authorized IP addresses and outbound IP ranges.
- Output a flattened SPF record within the 10-lookup limit and DNS character limit.
Step 4: Update Your DNS TXT Record
Replace your current SPF configuration in your DNS registrar’s management console with the new flattened SPF record. Ensure you retain SPF macros where necessary for features like geographic or special user routing (as permitted by email vendors such as Google Workspace or Microsoft 365).
Step 5: Test and Validate
Validate the new DNS TXT record using an SPF checker to confirm the flattened record returns an SPF pass under all expected authentication paths. Check for compliance with RFC 7208, adherence to the DNS lookup limit, and integrity of all third-party sender authorizations.
Step 6: Monitor Ongoing Compliance
Monitor your DMARC policy and SPF reporting for any new validation failures or silent SPF failures. Tools that offer centralized management and aggregated DMARC reports simplify ongoing SPF management and facilitate quick adaptation to provider or outbound IP address changes.
Best Practices, Risks, and Ongoing SPF Maintenance
Best Practices for Effective SPF Flattening
Use Hosted SPF and Dynamic Flattening
Leverage hosted SPF and dynamic SPF flattening solutions that automatically update your flattened SPF record as third-party vendors modify outbound IP ranges. Platforms like PowerSPF, integrated with the PowerDMARC dashboard, provide ongoing automatic updates and reduce the risk of manual errors.
Stay Within Character and Lookup Limits
Always ensure that your flattened SPF record remains under the DNS TXT record character limit and well within the 10-lookup limit.
Avoid Over-Flattening
While static SPF flattening streamlines configuration, over-flattening can make your SPF record brittle if you don’t have a mechanism for regular automatic updates—especially with email vendors and cloud services prone to periodic IP address changes.
Potential Risks and How to Mitigate Them
Manual Flattening and Maintenance Burden
Relying solely on manual flattening introduces a significant maintenance burden. As your service providers like Google or Microsoft update IP addresses, your SPF record may quickly become outdated, resulting in SPF failures and DMARC misalignment.
Automated Updates and Centralized Management
Automated SPF flattening tools with hosted SPF services minimize this risk by delivering real-time, centrally managed updates, preserving authentication standards and maximizing deliverability.
SPF Macros and Complex Mechanisms
Improper handling of SPF Macros or complex nested include chains can cause validation failures. Use trusted SPF flattening tools that can parse and retain legitimate SPF macros and flatten records without causing SPF PermError.
Routine Monitoring and Reporting
Implement regular SPF reporting and use aggregation tools for DMARC reports to monitor SPF pass/fail rates. Identify potential issues early—such as silent SPF failures or record bloat—that might degrade email delivery or trigger validation errors. Incorporate SPF auditing as part of your ongoing email authentication and SPF management processes to maintain optimal security and deliverability.
By adopting these strategies and leveraging AutoSPF, organizations can safely implement SPF flattening, maintain compliance with email authentication standards, and protect their email deliverability and sender reputation in an evolving cloud ecosystem.
